What if an unusually long password could give you access to an account with no password at all? It may sound like a joke, but that is exactly what made headlines in the OpenSSH community last week.
On November 5, OpenSSH released version 10.6p2 to address a critical vulnerability affecting Linux systems that use musl with PAM disabled. Known as *sshole, the flaw is identified as CVE-2026-123158 and carries a CVSS score of 8.1. It was reported by Özgün Kültekin from Wakefield.
Accounts that have no usable password contain an asterisk in /etc/shadow. According to Help Net Security, when the musl library processes a password exceeding 256 bytes, the crypt() function fails and returns an asterisk as well. When sshd compares the values, they match, and authentication succeeds.
(Free access, no subscription required)
According to Invadel’s summary, four conditions must be met simultaneously:
sshd must be running on musl with PAM disabled, as is the case with Alpine’s default package.
Password authentication must be enabled, which is the default setting.
The targeted account must have exactly one asterisk in /etc/shadow.
Another local account must have a SHA-crypt password hash.
Distributions using glibc, such as Debian and Ubuntu, are not affected.
One distinction matters here: password-based root login is only possible if an administrator has explicitly set PermitRootLogin yes. A more realistic target is the alpine account included in official cloud images, which can obtain root privileges through doas without entering a password.
According to Invadel’s summary, four conditions must be met simultaneously:
sshd must be running on musl with PAM disabled, as is the case with Alpine’s default package.
Password authentication must be enabled, which is the default setting.
The targeted account must have exactly one asterisk in /etc/shadow.
Another local account must have a SHA-crypt password hash.
Distributions using glibc, such as Debian and Ubuntu, are not affected.
One distinction matters here: password-based root login is only possible if an administrator has explicitly set PermitRootLogin yes. A more realistic target is the alpine account included in official cloud images, which can obtain root privileges through doas without entering a password.
Soon after, Previdian reported the first attempt within nine hours of the CVE’s publication. By November 8, it had logged 20 attempts from 13 IP addresses.
So we asked ourselves the obvious question: was this reaching our region too?
What We Observed in Our Honeynet
At LACNIC’s CSIRT, we operate a network of Cowrie honeypots across Latin America and the Caribbean. Cowrie simulates an SSH server and records the credentials it receives. We therefore searched for passwords containing 257 characters or more across the sensors already integrated into our analysis platform.
Some results appeared to be TLS connections recorded as binary credentials, with their length inflated by the way they were stored. Our first task, therefore, was to clean the data.
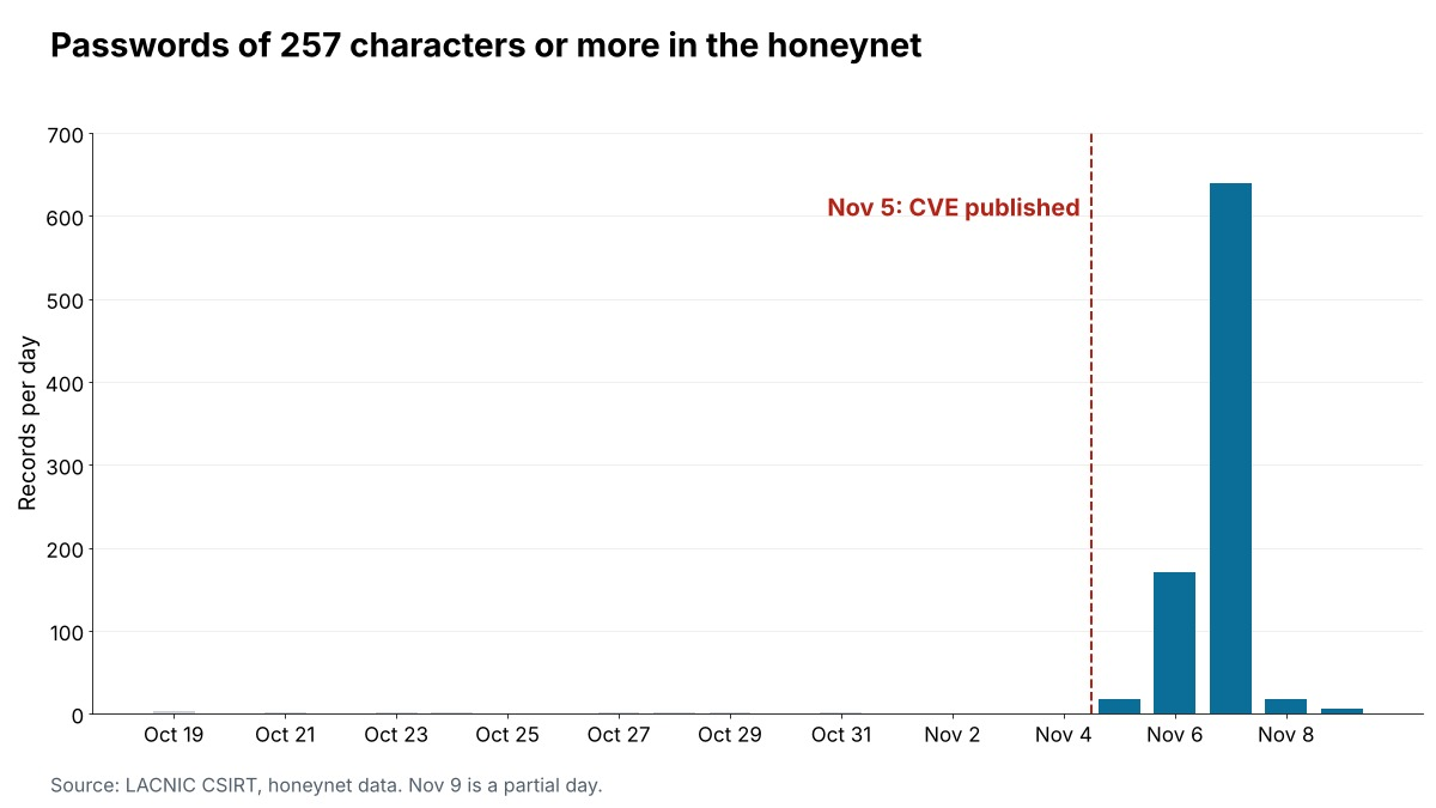
Between October 19 and 31, there were only 12 records with long passwords, and those we examined turned out to be this type of noise. From November 1 to 4, there were none. Starting November 5, we observed 852 records, with a peak of more than 600 on November 7.
Of those 852, 849 were plaintext passwords, each sent in a different SSH session.
666 were exactly 257 characters long, the minimum length required to trigger the bug.
768 began with repeated letter As.
773 targeted root and 52 targeted alpine.
That last figure is striking: the vast majority of attempts went after root, which does not accept passwords on a default Alpine install, and very few targeted the alpine user. Whoever is scanning at scale does not seem to be fine-tuning their targets much.
Most sessions came from a single IP address, while other sources spread their attempts across numerous sensors. Among the most active IP addresses, the earliest activity was recorded at 17:17 UTC on November 5, roughly 90 minutes after the CVE became public.
What happened once they got in?
Because Cowrie allowed the connections, we could examine the attackers’ next steps. Almost half of the sessions ended without running a single command, which would be consistent with attempts to verify whether authentication had succeeded. The remaining sessions included command execution, revealing four patterns of behavior:
Reconnaissance using netstat, reading /proc/net/tcp, and using markers to determine whether the shell was genuine.
Downloading a script designed to terminate competing processes, including hidden ones, and deploy a bot targeting 15 different architectures, using the label alpine. VirusTotal shows detections by 30 of 61 security engines, and the script had been analyzed even before the CVE was disclosed. The x86_64 binary is classified as gafgyt/mirai.
Persistence through two files written to each sensor. In the cases we checked, they were an SSH key pair, which points to access set up per victim. Some sessions also attempted to open a reverse SSH tunnel back to the same IP they came in from.
These behaviors originated from different sources. Although we cannot attribute the activity to specific actors, the evidence does not suggest a single coordinated campaign.
Recommended Actions
If you administer systems using musl or Alpine-based images running sshd, we recommend the following:
1. Update and restart Install OpenSSH 10.6p2 or the patched package provided by your distribution, and restart sshd, as the running process will continue using the previous binary.
2. Mitigate if You Cannot Update
Disable password authentication by setting PasswordAuthentication no, as recommended by OpenSSH’s Damien Miller.
3. Review Look for Accepted password for in accounts without a password, and check authorized_keys, recently created users, and doas usage, as recommended by Alpine.
Within just hours, a public advisory had turned into real traffic hitting sensors in our region. What caught our attention most, however, was the initial script, which already existed before the CVE was published.
The operators behind this botnet simply changed their initial access method, one of the tactics in the MITRE ATT&CK framework. They already had the rest of the attack chain in place.
Figure 1. Daily count of passwords 257 characters or longer logged by the honeynet. Data for November 9 is partial. Credit: LACNIC CSIRT.